SEC-015
Cloudflare WAF rule configuration
Cloudflare's firewall configured to filter attacks before they reach your server at all.
Standard Dashboard / config
Needs: CDN access

Showing fixes 113–128
Cloudflare's firewall configured to filter attacks before they reach your server at all.
Colour combinations that fail WCAG contrast, corrected while staying close to your brand palette.
Your comment system configured properly — spam filtering, moderation rules, and notification settings set up to match how you actually want to run it.
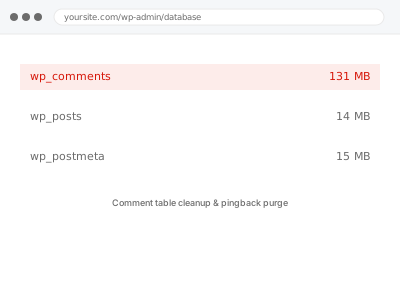
Your comments table is carrying years of uncleared spam, trash and pingbacks. We clear the backlog safely and configure settings so it doesn't rebuild.
Conditional fields that show, hide, or contradict incorrectly — traced through every real combination.
Real visitor scenarios tested against your cookie consent banner — before consent, after accepting, after declining — to confirm it behaves correctly.
Consent Mode v2 connected to your actual cookie banner, so Google's tags behave the way you've already told visitors they would.
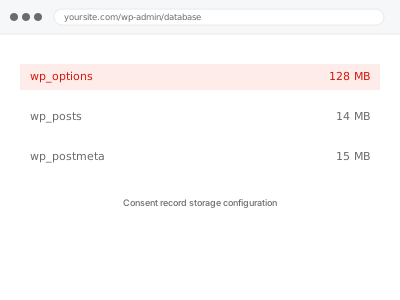
Consent choices recorded reliably, so you can show what a visitor agreed to, and when.
Scripts still running after a decline — found and genuinely gated behind real consent.
Your name, address, and phone number made identical everywhere it appears sitewide.
Contact form entries arrive but the email notification behind them doesn't — we trace where the handoff actually breaks.
Drip-fed content stuck on the wrong schedule, traced to the actual date or timezone calculation behind it.
Up to 20 pages rewritten for clarity and extraction — same facts, more directly stated.
Up to 50 pages rewritten for clarity and extraction — same facts, more directly stated.
Every page and post inventoried in one spreadsheet — title, type, word count, status.
Content sitting in the wrong post type — pages that should be posts, products that should be a custom type. We migrate it across cleanly.